
Inside and outside.
One platform.
Continuous external attack-surface monitoring — subdomains, exposed ports, certs and configs, all verified-owned. Authenticated API and GraphQL scanning with a production safe-mode. Internal discovery that knows a phone from a printer. Plus a full suite of industry-standard scanners behind one dashboard, EPSS and CISA KEV intelligence, and optional AI-assisted routing.
Full Suite
Scanners
External + Internal
Coverage
EPSS + KEV
Intelligence
BYO AI
Any model
How it works
Deploy. Scan. Watch. Triage.
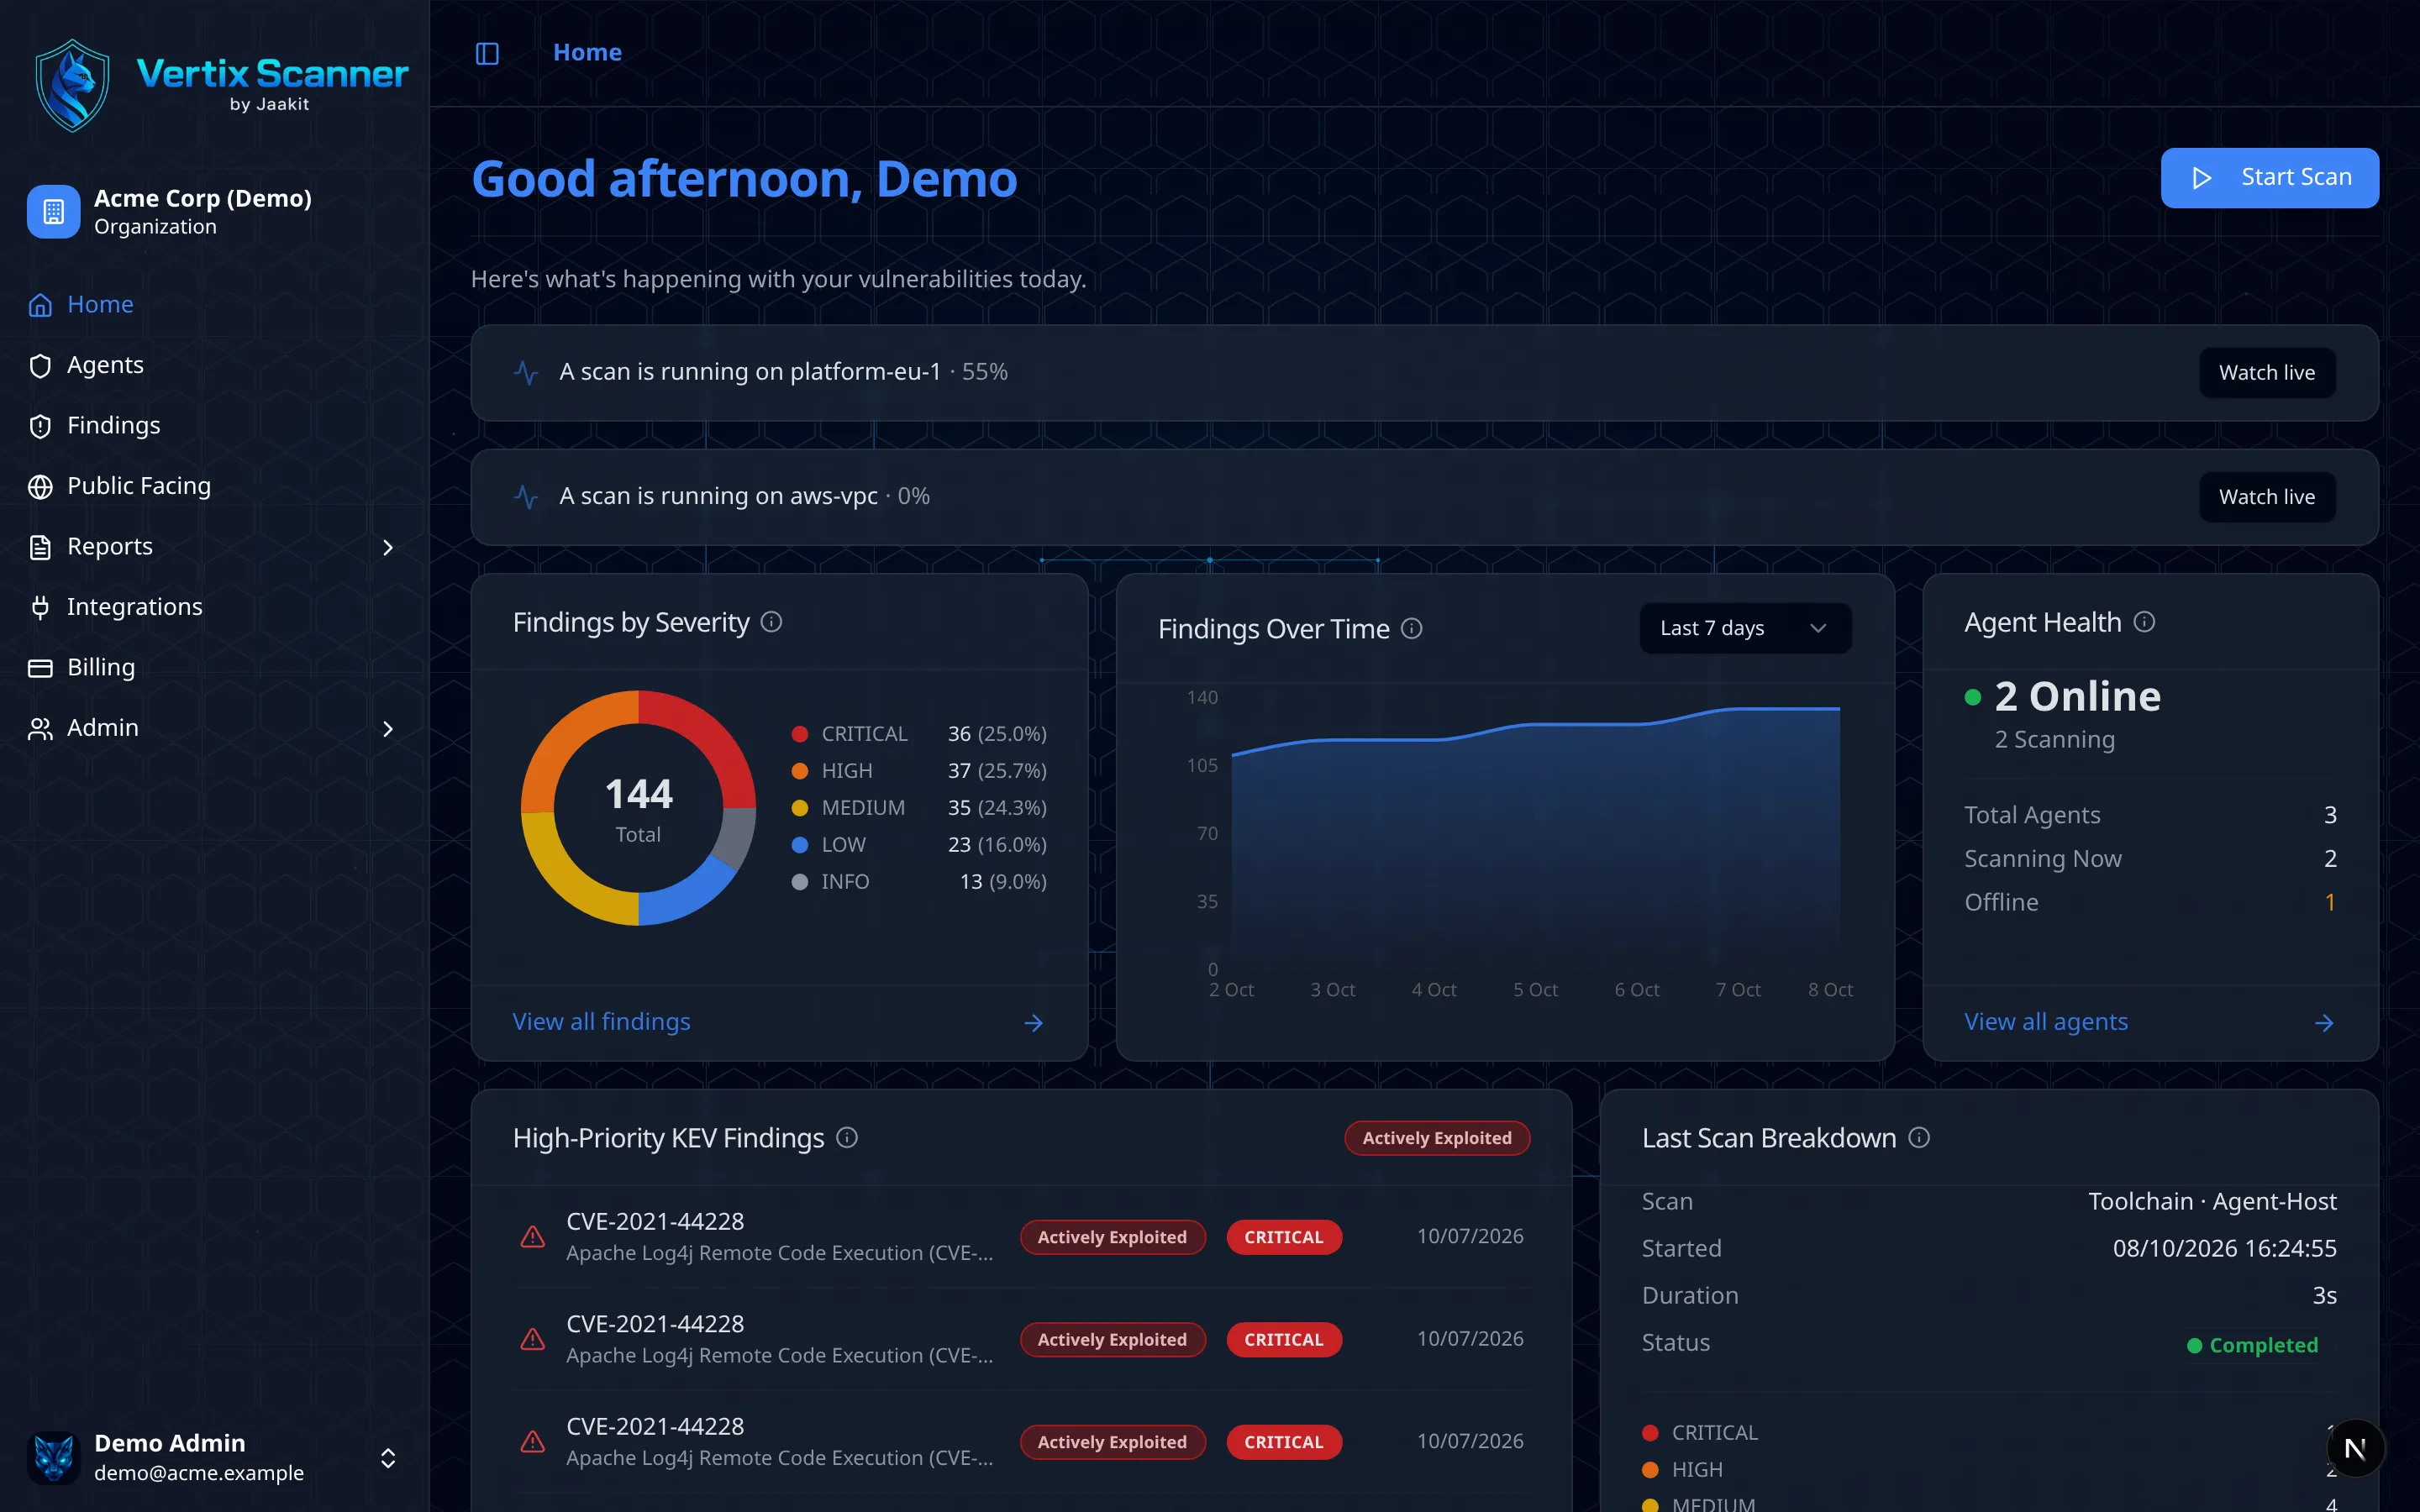
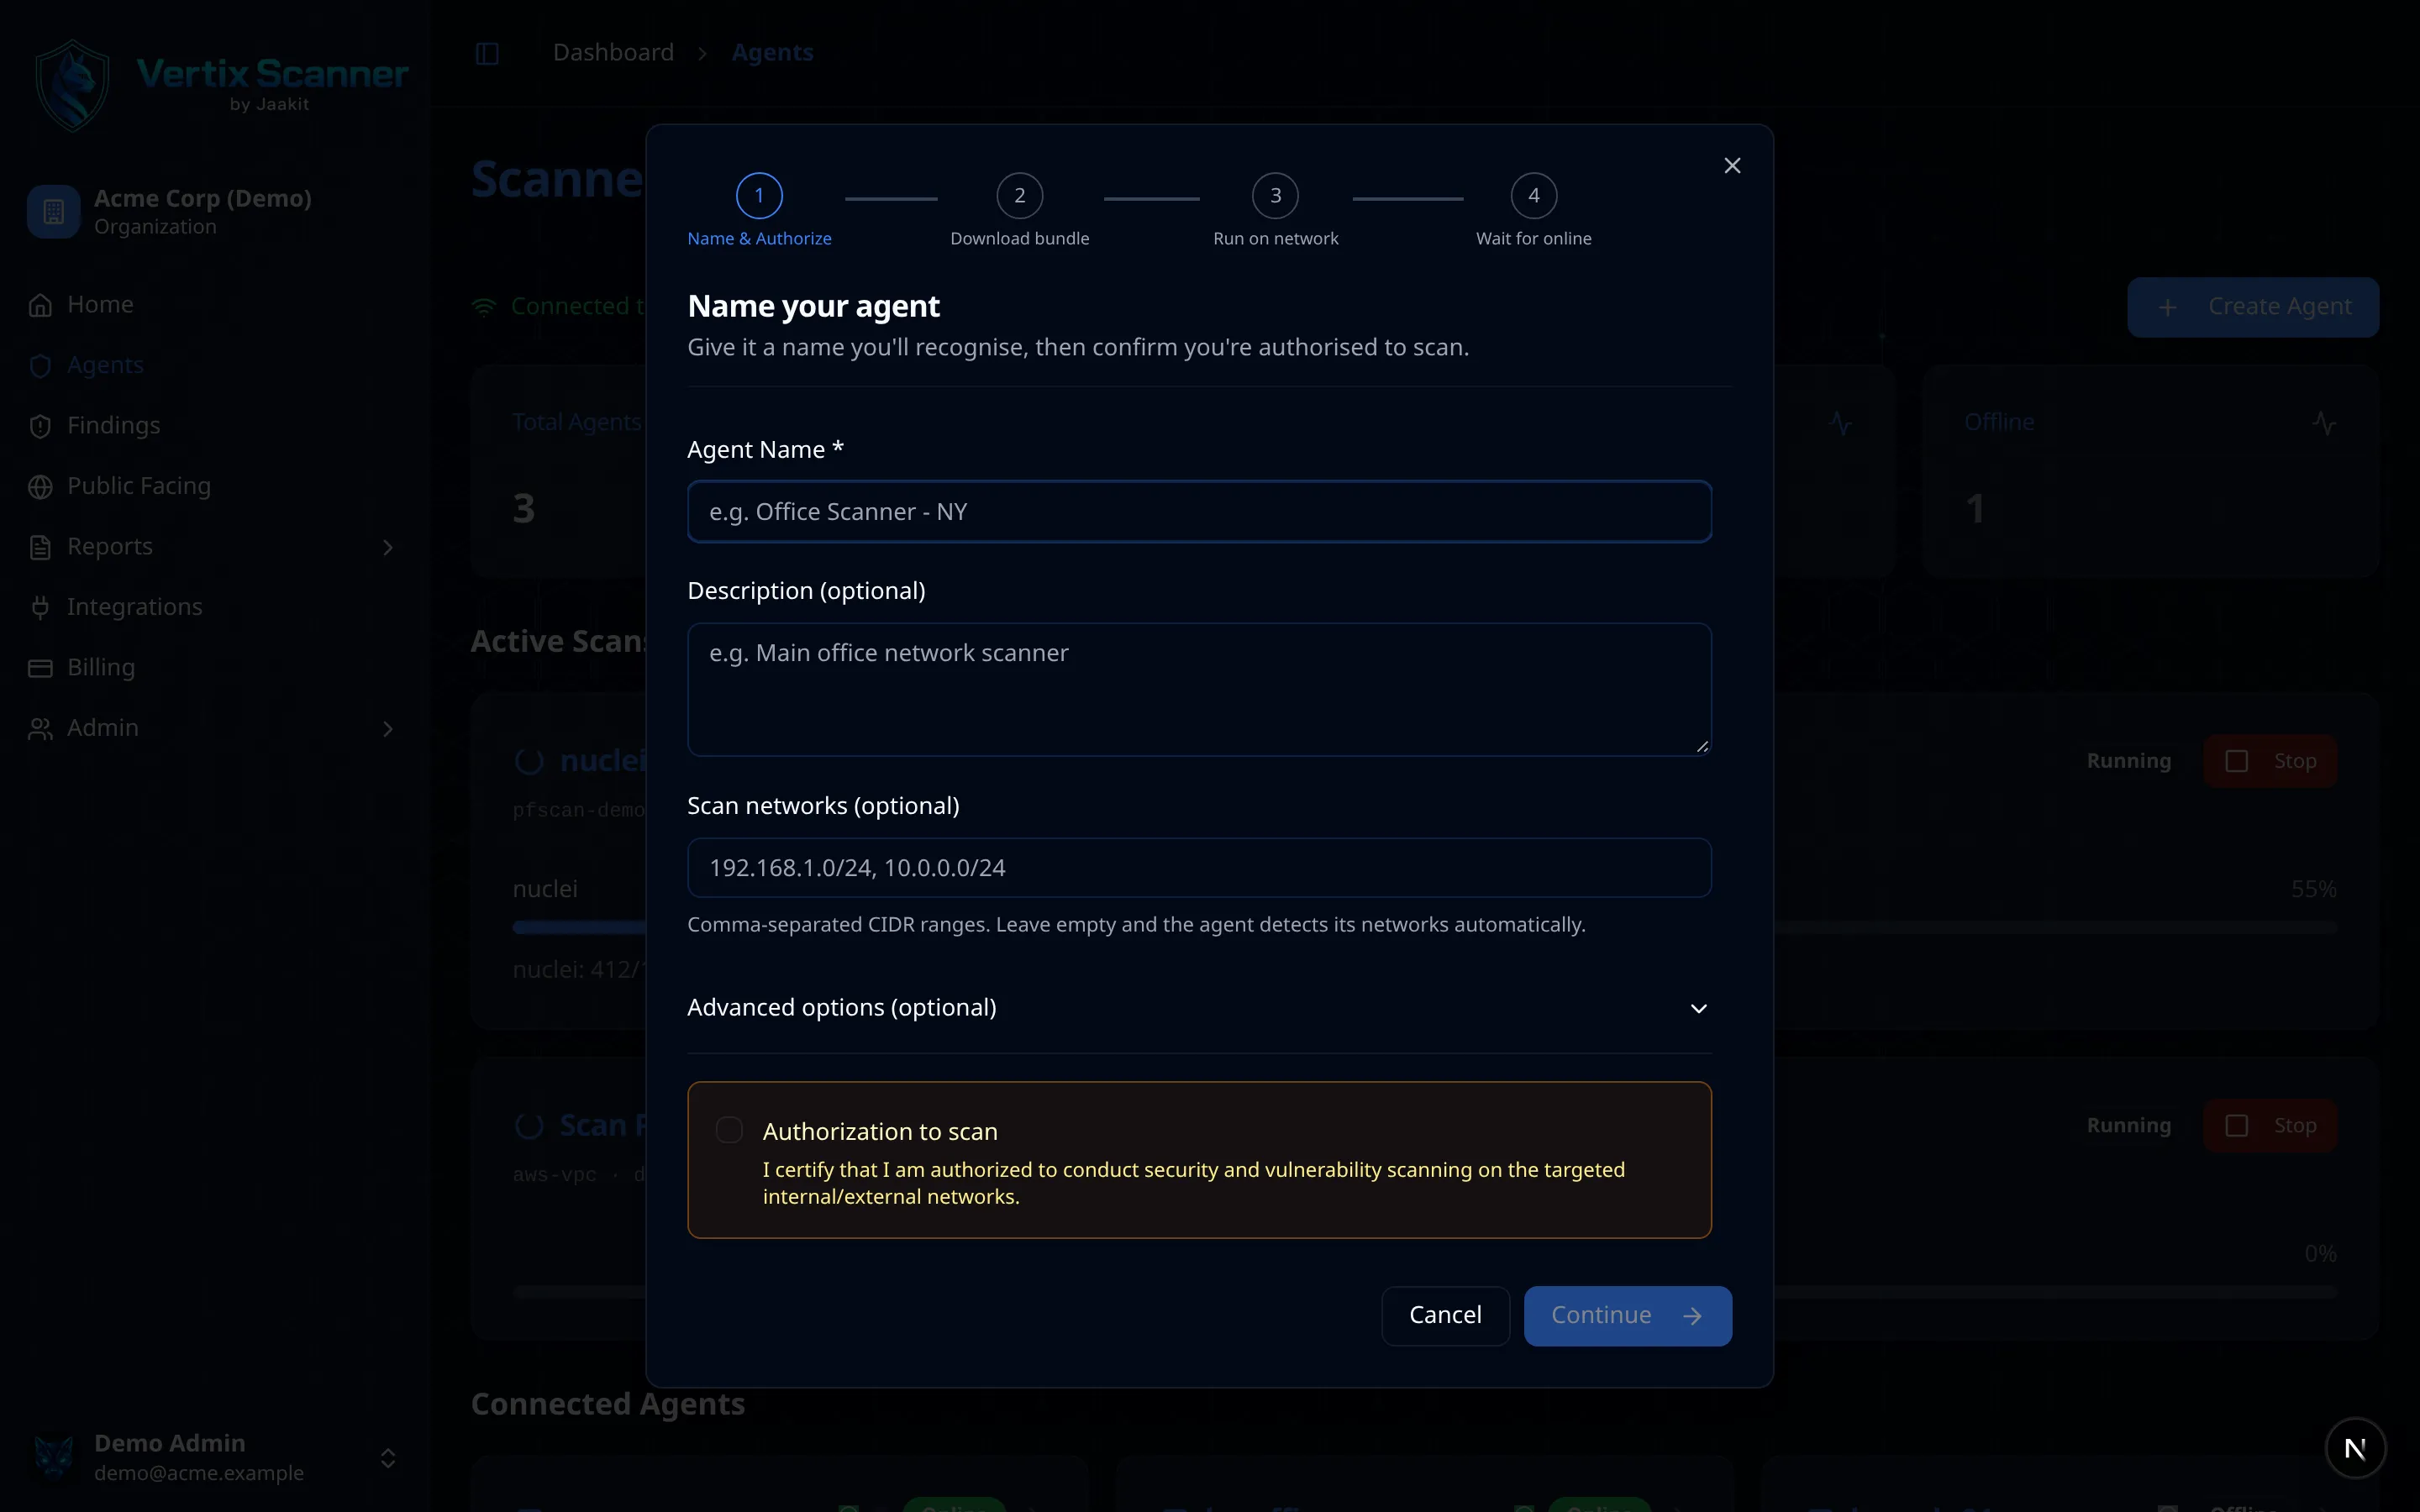
Real screenshots from a live demo environment — not mockups.
Why it matters
Severity alone lies to you
CVSS tells you how bad it could be. EPSS and CISA KEV tell you whether anyone is actually exploiting it. Toggle to see the difference.
- 110.0Apache Struts OGNL injectionKEVEPSS 97%
- 29.8TLS 1.0 enabled on mail gatewayEPSS 2%
- 39.8vsftpd backdoor (CVE-2011-2523)KEVEPSS 91%
- 49.1Unauthenticated Redis instanceEPSS 62%
- 57.2SSH weak key-exchange algorithmsEPSS 1%
- 65.3Missing Content-Security-PolicyEPSS 5%
Sorted by severity, the top item looks scary — but a 2% exploit chance and a local-only attack surface mean it can wait.
Architecture
Two paths — an agent inside,
the platform outside
For internal scanning, the Vertix agent runs inside your perimeter and initiates every connection — your firewall stays closed. For external scanning, the platform probes only assets you've verified ownership of.
Vertix Cloud
app.jaakit.com
- Dashboard, findings, reports
- Scan scheduling & SIEM export
- AI routing & EPSS/KEV enrich
- Public scans of verified assets
outbound-only
encrypted
Your network
agent runs inside
- Docker / VM / bare metal
- Scans local subnets & hosts
- Results encrypted in transit
vs. rolling your own
A full toolchain's worth of plumbing, already done
| DIY toolchain | Vertix Scanner | |
|---|---|---|
| Setup | Install and configure every scanner yourself | One agent deploy — scanners pre-integrated |
| Output | A different format per tool, manual parsing and deduplication | Normalized findings, deduplicated automatically |
| External exposure | Separate tools for DNS, certs and ports — no history | Verified, scheduled, with change feed and score |
| Safety | Easy to scan something you don't own | Ownership proof, denylist, audit log |
| Prioritisation | CVSS only — you guess what's actually exploitable | EPSS + CISA KEV enrichment on every finding |
| History | Scattered output files, no trend tracking | Trends, schedules, suppression with audit trail |
| Reporting | Write your own exec summaries | PDF export + scheduled email reports |
| Integrations | Roll your own SIEM/Slack plumbing | Splunk, Syslog/CEF, webhooks, Slack built in |
External Attack Surface
See your perimeter the way an attacker does
Vertix continuously maps and monitors everything your organization exposes to the internet — subdomains, ports, certificates, email and web configuration — and flags what needs attention first.
Requires verified ownership — you can only scan what you prove is yours
API Security
REST and GraphQL, scanned with credentials, safely
Declare APIs as first-class assets and run authenticated DAST against them — with a production safe mode that keeps destructive checks off your live endpoints.
Authenticated API scanning Growth+
Continuous Monitoring
Know when your attack surface changes
One scan is a snapshot; monitoring is a feed. Vertix re-checks your external footprint on a schedule and tells you the moment something new appears.
Internal Discovery
Knows a phone from a printer
The agent maps your internal network — actively and passively — classifies every device it finds, and alerts you the moment something unknown joins.
Scanner Arsenal
A Full Suite of Industry-Standard Scanners
Unified under one orchestration layer — no tool sprawl, no context switching.
naabuStarter
Fast TCP port discovery
NmapStarter
Service/version detection + NSE vuln scripts
NucleiStarter
Template-based vulnerability scanning
NiktoStarter
Web server misconfiguration scanner
WhatWebStarter
Web technology fingerprinting
testssl.shStarter
SSL/TLS configuration testing
ssh-auditStarter
SSH server security auditing
MasscanGrowth+
High-speed port scanning for large networks
OpenVAS/GVMGrowth+
Deep comprehensive vulnerability assessment
WapitiGrowth+
Black-box web application (DAST) scanner
TrivyGrowth+
Container, filesystem & IaC scanning
OWASP ZAPGrowth+
Dynamic application security testing
sslyzeGrowth+
Fast SSL/TLS scanner
Platform
Core Capabilities
Everything needed to run, manage, and act on vulnerability data at scale.
Intelligence
Exploitability-Driven Triage
Not all vulnerabilities are equal. Vertix Scanner combines EPSS, CISA KEV, and CVSS into a composite triage score — so your team focuses remediation effort where it matters most.
EPSS Integration
Exploit Prediction Scoring System data predicts the likelihood of exploitation in the wild.
CISA KEV Catalog
"Actively Exploited" badges instantly surface vulnerabilities with known active exploitation.
Composite Triage Score
KEV override + EPSS×CVSS bucketing produces actionable triage tiers with SLA tracking.
Finding Lifecycle
Open → Fixed → Ignored states with remediation guidance, references, and false positive management.
Triage Queue — Live
Architecture
Distributed Agents
Deploy lightweight agents inside any network — on-premise, air-gapped, or hybrid. Agents operate independently, queue results offline, and reconnect automatically.
- Docker & native Linux binary deployment
- Auto-discovery of installed scanner tools
- Persistent result queue survives restarts
- Offline operation — queues when backend unavailable
- Real-time health monitoring & version tracking
- API key rotation & auto-update with signature verification
Integrations
SIEM & API
Push findings directly to your SIEM with EPSS and KEV enrichment, notify the team over Slack or email, or pull via the versioned REST API with cursor-based pagination and machine API keys.
- JSON, NDJSON, CEF output formats
- Cursor-based pagination & since parameter
- HMAC-authenticated webhooks
- Scheduled delivery with dead-letter queue & retry
Reporting
Reporting & Analytics
From prioritized findings PDFs to technical drill-downs — plus scheduled delivery straight to stakeholders' inboxes.
Findings Reports
Prioritized findings with severity, EPSS, KEV and triage tiers — exported as PDF from the dashboard.
Technical Scan Reports
Detailed internal & external scan reports for engineering teams.
Scheduled PDF Delivery
Reports emailed automatically on your cadence (Growth+).
Trend Analysis
Track security posture and fix times over time.
API Export
JSON, NDJSON and CEF via the versioned pull API.
Security
Security & Compliance
Enterprise-grade security controls, audit logging, and report evidence that supports your compliance programme.
Compliance report mappingsComing soon
Finding and remediation reports mapped to SOC 2, HIPAA, PCI DSS and GDPR control families — to help assemble audit evidence.
- Session auth + rate-limited sign-in (MFA coming soon)
- Audit logging with full request context
- Encrypted per-org notification & integration secrets
- TLS enforced in production
Who It's For
Built For Every Team
- Continuous monitoring
- Compliance reporting
- Risk management
- Team collaboration
- Multi-tenant support
- White-label reports
- Scalable architecture
- Automated workflows
- CI/CD integration
- Container scanning (Trivy)
- Infrastructure as code
- Fast feedback
- Easy Docker deployment
- Cost-effective
- All scanners included
- Professional support
Get Started
Ready to Unify Your Security Stack?
Vertix Scanner consolidates a full scanner suite, enriches findings with EPSS and KEV intelligence, and integrates directly with your SIEM — all from a single platform.
AI-Assisted Scanning
The Agent Is AI Capable
Vertix Scanner's distributed agent can integrate your own local or cloud-hosted AI model to help decide which tools to run against each discovered target. You stay in control of the model, the endpoint, and how much influence the AI has over the agent's behavior.
Local or cloud
Ollama, LM Studio, OpenAI, Anthropic, or any OpenAI-compatible API.
Three behavior modes
Advisory, assist, and autonomous with rule-based fallback.
Finding analysis — Growth+
AI prioritises findings and flags likely false positives with a rationale.
Verification & remediation — Pro+
Allow-listed, non-destructive checks confirm findings; AI fix guidance is validated by a targeted re-scan.
Guard-railed output
AI plans are filtered by enabled tools, allowed tools, and max-tools-per-target limits.
No vendor lock-in
Swap models or endpoints from the dashboard at any time.
Gallery
Every screen, unretouched
Captured from the same demo environment — click to enlarge.
Video
See it in motion
Product walkthrough
Video coming soon — meanwhile, take the live tour or request a demo.
See a real findings report
The same PDF your team can export or schedule: prioritized findings, EPSS and CISA KEV exploitability, triage tiers and remediation status — generated from real scan data in the demo environment.
Scheduled email reports · Growth & above